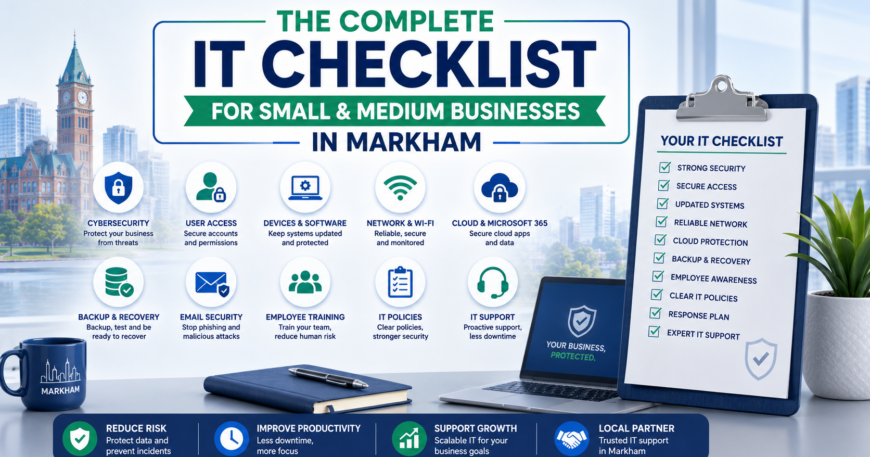
Technology is now part of almost every business process, from communicating with customers and managing finances to storing documents and processing transactions. For small and medium businesses in Markham, keeping that technology secure, reliable, and properly maintained can become difficult as systems grow and new tools are added. A practical IT checklist helps business owners identify gaps before they turn into downtime, security incidents, or unexpected costs.
The checklist below covers the core areas every Markham SMB should review, including cybersecurity, devices, networks, cloud services, backups, employee access, and IT support. It is based on recommendations from the Canadian Centre for Cyber Security and common requirements for businesses managing modern IT environments.
1. Know What Technology Your Business Actually Uses
You cannot properly protect systems you don’t know you have.
Start by creating an inventory of your IT environment, including:
- Desktop computers and laptops
- Smartphones and tablets
- Servers and network equipment
- Printers and other connected devices
- Microsoft 365 and other cloud applications
- Business software and SaaS platforms
- Websites and online services
- External storage and USB devices
Record who uses each device or application and what business information it contains. The Canadian Centre for Cyber Security specifically recommends that SMBs identify the information systems and assets within their environment and assess their importance to the business.
Checklist: ☐ Maintain an updated IT asset inventory
2. Review Your Cybersecurity Defenses
Cybersecurity should be one of the first items on your checklist.
Check whether your business has protection across endpoints, email, networks, cloud applications, and user accounts. Antivirus software alone isn’t enough for a modern business environment.
Your cybersecurity checklist should include:
- Endpoint protection
- Email security
- Firewall protection
- Multi-factor authentication (MFA)
- Secure device configurations
- Regular vulnerability reviews
- Security monitoring
- Employee security awareness training
- Incident response procedures
The Canadian Centre for Cyber Security recommends SMBs prioritize strong authentication, security software, patching, backups, employee training, access controls, and secure cloud services.
Checklist: ☐ Review your cybersecurity controls at least annually
Don’t Forget About Phishing
Employees remain an important part of your security strategy. Regular training should teach staff how to recognize suspicious emails, links, attachments, impersonation attempts, and unusual payment requests.
3. Make Sure Every Account Is Properly Secured
User accounts provide access to business systems, files, email, and sensitive information.
Review your accounts regularly and remove access when employees leave. Also check whether former employees, contractors, vendors, or inactive accounts still have unnecessary permissions.
Your IT checklist should include:
- MFA enabled on important accounts
- Strong, unique passwords
- Password manager where appropriate
- Separate administrator accounts
- Least-privilege access
- Regular access reviews
- Immediate account deactivation for departing employees
Pay particular attention to Microsoft 365, financial applications, CRM systems, cloud storage, and remote access tools.
Checklist: ☐ Review privileged and inactive accounts regularly
4. Keep Devices and Software Updated
Outdated software creates avoidable security and reliability problems.
Your IT team or provider should have a defined patch management process covering operating systems, applications, firmware, browsers, security tools, and network equipment.
Don’t forget hardware either. Older computers and servers can become difficult to support and may eventually stop receiving security updates.

The Cyber Centre recommends automatically patching operating systems and applications where possible, making patch management a fundamental control for Canadian SMBs.
Checklist: ☐ Enable automated updates where appropriate
Checklist: ☐ Track devices approaching end of life
5. Check Your Network and Wi-Fi
Your network is the foundation connecting employees, devices, cloud applications, and customers.
Review whether your firewall is properly configured and whether your business Wi-Fi is secure. Guest networks should be separated from internal business systems, while network equipment should receive regular firmware updates.
Check for:
- Business-grade firewall
- Secure Wi-Fi configuration
- Separate guest network
- Updated network equipment
- VPN or secure remote access where required
- Network monitoring
- Appropriate bandwidth
- Network segmentation for sensitive environments
A slow or unreliable network isn’t always an internet-provider problem. Aging equipment, poor Wi-Fi coverage, configuration issues, and excessive traffic can all affect performance.
Checklist: ☐ Review network performance and security
6. Audit Your Microsoft 365 and Cloud Environment
Cloud applications have made it easier for SMBs to work from almost anywhere, but they still need proper management.
So, the 6th IT checklist point is to review user permissions, administrator accounts, MFA, sharing settings, security policies, and connected applications. Make sure former employees no longer have access and that sensitive documents aren’t being shared publicly or with unnecessary external users.
Also remember that using a cloud platform doesn’t automatically mean every business data-recovery requirement is covered.
If your business relies heavily on Microsoft 365, your checklist should include:
- Exchange Online
- OneDrive
- SharePoint
- Microsoft Teams
- User permissions
- Administrator accounts
- Security policies
- Backup and recovery
Read more: Protecting Microsoft 365 Data with Microsoft 365 Backup
Checklist: ☐ Conduct a Microsoft 365 security and access review
7. Test Your Backup and Disaster Recovery Plan
Having backups is only part of the equation. You also need to know whether you can actually restore your data.
Your backup checklist should answer:
- What data is backed up?
- How frequently are backups performed?
- Where are backup copies stored?
- Are backups protected from ransomware?
- How long are backups retained?
- When was the last restore test?
- Who is responsible for recovery?
- Which systems must be restored first?

Statistics Canada reported that 13% of Canadian businesses affected by cybersecurity incidents experienced ransomware in 2023, up from 11% in 2021.
A tested recovery plan can make the difference between a manageable interruption and a prolonged business shutdown.
Checklist: ☐ Perform regular backup restoration tests
8. Secure Remote and Mobile Work
Employees may access company systems from homes, client sites, airports, or other locations.
That means your IT checklist should cover devices and connections outside the office as well.
Make sure:
- Company laptops are encrypted
- Mobile devices have screen locks
- MFA is required
- Remote access is secured
- Lost devices can be remotely disabled or wiped
- Employees know how to use public Wi-Fi safely
- Personal devices follow defined security requirements
The Cyber Centre includes secure mobility among its recommended baseline controls for Canadian SMBs.
Checklist: ☐ Review remote-work and mobile-device security
9. Prepare Employees for IT and Security Issues
Employees need clear instructions for what to do when something goes wrong.
Create simple procedures covering phishing emails, suspicious downloads, lost devices, unusual account activity, accidental data sharing, and suspected malware.
Training doesn’t need to be complicated. Short, regular sessions are often easier for employees to absorb than an annual information dump.
Checklist: ☐ Provide recurring cybersecurity awareness training
10. Have an Incident Response Plan
What happens if your business discovers ransomware at 9 a.m. on a Monday?
Everyone should know the answer before that situation occurs.
Your incident response plan should identify:
- Who has authority to make decisions
- Who contacts your IT provider
- Who communicates with employees
- Who handles customers and vendors
- How compromised devices are isolated
- Where backups are accessed
- When legal or regulatory advice is required
- When law enforcement should be contacted
The Canadian Centre for Cyber Security recommends that SMBs develop an incident response plan and connect it with business continuity and disaster recovery planning.
Checklist: ☐ Document and test your incident response process
11. Review Your IT Costs and Technology Lifecycle
IT budgeting shouldn’t consist of waiting for something to break.
Create a basic technology roadmap covering hardware replacements, software renewals, cybersecurity investments, cloud projects, network upgrades, and other major expenses.
Look for equipment approaching end of life and software that will no longer receive support. Planning these replacements ahead of time can help prevent emergency purchases and unexpected downtime.
Checklist: ☐ Maintain a 12–24 month IT investment plan
12. Decide Who Is Responsible for IT
Finally, every SMB needs clear ownership.
Someone should be responsible for reviewing security alerts, managing access, checking backups, handling vendors, tracking equipment, and coordinating IT projects. This doesn’t necessarily mean hiring a full-time IT employee.
Many smaller organizations use an external IT provider for specialized expertise and day-to-day management. The Cyber Centre notes that smaller organizations may not have the capacity to perform some security activities internally and may use contracted services instead.
A managed IT provider can take responsibility for ongoing monitoring, maintenance, cybersecurity, help desk support, cloud management, backup, and strategic IT planning.
Checklist: ☐ Define who owns each major IT responsibility
When Should You Review Your IT Checklist?
An IT checklist shouldn’t be something you complete once and forget.
Review it at least annually and whenever your business experiences a major change, such as:
- Moving to a new office
- Hiring several employees
- Launching new software
- Moving more systems to the cloud
- Acquiring another company
- Experiencing a security incident
- Replacing major infrastructure
- Changing IT providers
Your IT environment changes as your business changes, so your checklist needs to change with it.
How Sun IT Solutions Can Help Markham SMBs
Managing every item on this checklist internally can be difficult when your team is already focused on running the business. At Sun IT Solutions, we help businesses in Markham manage the day-to-day technology behind their operations through managed IT services, cybersecurity, Microsoft 365 support, cloud services, network management, backup and disaster recovery, and help desk support.
Our approach focuses on keeping technology secure, maintained, and aligned with your business needs instead of waiting for problems to disrupt your team. We can also help identify gaps in your current IT environment and prioritize the improvements that make the most sense for your budget and goals.
For businesses that need ongoing support, we provide proactive monitoring and technical assistance alongside strategic IT planning. Book your free consultation with Sun IT Solutions and let us help you turn this IT checklist into a practical IT plan for your Markham business.
